
Signal, Not Noise
Add rich context on-stream to power your detections.
Security data pipelines route telemetry but do not add the required context to uncover threats. AlphaSOC enriches raw events with threat intelligence and reputation scoring. With no threat feeds or lookup tables to maintain, you can focus on building effective detections.
Detect
Enrich
Scoring
Scoring
You’re not seeing the complete picture
Alerts often land in the queue without context: no prevalence metrics, no threat intelligence, no reputation score, and no verdict. Security teams patch these gaps with third-party APIs and threat feeds, but these are wired-in after the fact, adding further cost and complexity.Add Rich Context
AlphaSOC normalizes your telemetry to OCSF and enriches events with prevalence, threat intelligence, and real-time reputation data.
Your team receives complete detection findings, including evidence, that correlate back to raw events stored in a unified, open format within our data lake.
A Managed Security Data Platform
Integrate your existing tools with our platform to find threats before they become incidents.
Six Dimensions of Analysis
AlphaSOC normalizes and enriches every event. Detection logic is then applied to uncover anomalies and threats.
Intelligence Correlation
We check telemetry against 1M curated, live indicators from 70+ commercial and open sources.
Harness Field-Tested Detections
AlphaSOC maintains a comprehensive library of managed detections that align with MITRE ATT&CK to highlight known threat actor tactics, techniques, and procedures.


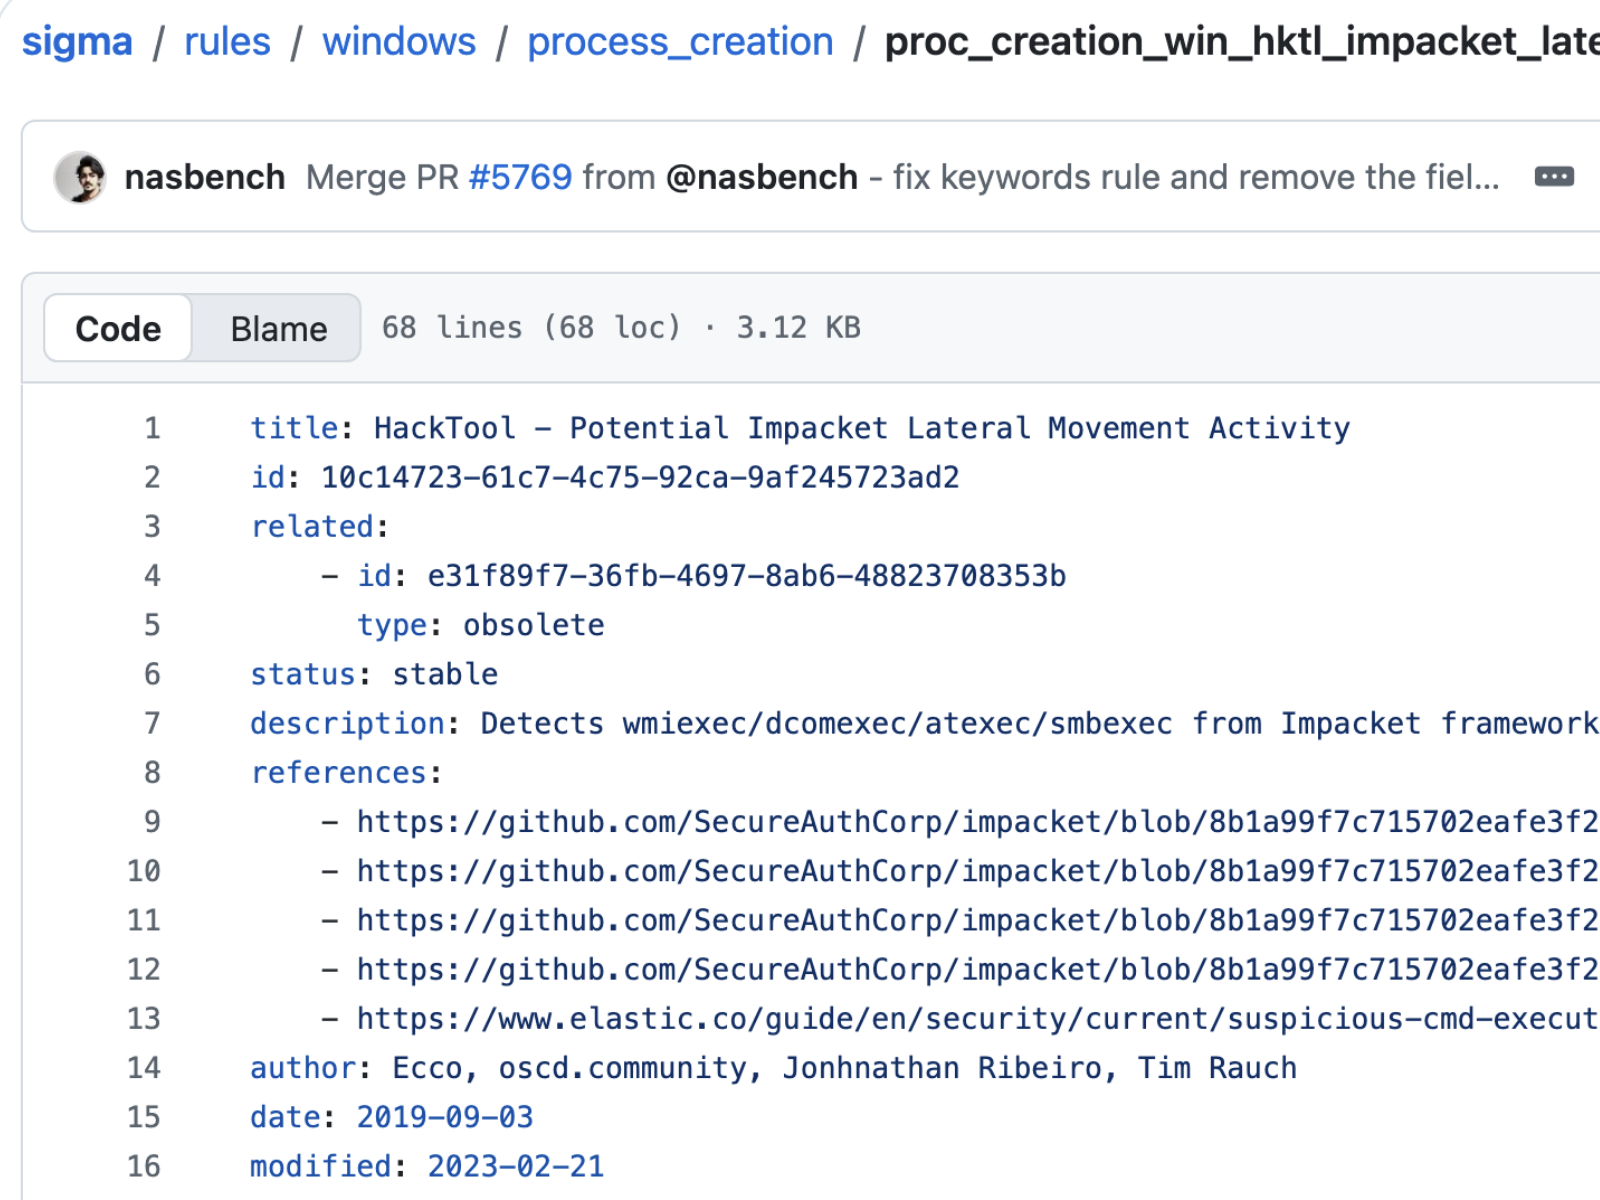
Detect Anything™
with Sigma Rules
Sigma is an open source YAML format used to create and share detection rules. We enable threat hunters to quickly deploy new rules and uncover emerging threats within their cloud, application, network, and endpoint logs.
Our detection engine natively supports Sigma, meaning there is no need to translate rules into a proprietary query language (e.g., KQL or SPL) before use.
Offload expensive processing to a dedicated engine
Complex detection logic doesn’t belong inside a traditional SIEM. AlphaSOC processes telemetry before it reaches your stack to deliver context-rich detection findings to your team. There are no lookup tables to maintain, no threat feeds to set up, and no classifiers to build.Measurable Benefits
The benefits are not abstract. Each traces directly to a specific capability.
Rich context
Enrich data before scoring, not during triage. AlphaSOC findings carry prevalence, threat intelligence, and reputation data. Analysts and agents get rich context to power their hunts and investigations.
Wide coverage
Overlay our in-built detections and your own custom Sigma rules with MITRE ATT&CK to uncover both known and unknown threats across cloud workloads, applications, networks, and endpoints.
AI-ready
AlphaSOC stores prevalence, reputation, and threat intelligence data using OCSF, not freeform text. AI agents reason over the same enriched data your analysts do, with no extra lookup step.
Cost control
We undertake Internet-wide scans and operate a threat intelligence platform with 1M+ curated indicators from 70+ sources. There are no additional threat feeds or third-party API keys to purchase.
Work with Enriched Data
Add context to your cloud, application, network, and endpoint logs with AlphaSOC’s threat intelligence and reputation scoring to drive effective detections, threat hunts, and investigations.